Hello,
I am working on a new update for one of our marketplace apps and have encountered the following issue:
-
fdk run(with or without tunneling via ngrok, does not matter). - I open the custom configs page - http://localhost:10001/custom_configs (or an ngrok link e.g. https://e31718229926.ngrok.io/custom_configs ). All tested URLs are present in the 3rd party platform’s Valid OAuth Redirect URIs list.
- The OAuth redirect happens and I successfully authorize in the 3rd party platform.
- At the moment I am redirected back to the http://localhost:10001/custom_configs (or the ngrok url), I get the following error in the web browser (+ it is logged in the terminal with fdk):
TokenError
    at OAuth2Strategy.parseErrorResponse (C:\Users\Ilya\AppData\Roaming\nvm\v10.18.0\node_modules\fdk\node_modules\passport-oauth2\lib\strategy.js:358:12)
    at OAuth2Strategy._createOAuthError (C:\Users\Ilya\AppData\Roaming\nvm\v10.18.0\node_modules\fdk\node_modules\passport-oauth2\lib\strategy.js:405:16)
    at C:\Users\Ilya\AppData\Roaming\nvm\v10.18.0\node_modules\fdk\node_modules\passport-oauth2\lib\strategy.js:175:45
    at C:\Users\Ilya\AppData\Roaming\nvm\v10.18.0\node_modules\fdk\node_modules\oauth\lib\oauth2.js:191:18
    at passBackControl (C:\Users\Ilya\AppData\Roaming\nvm\v10.18.0\node_modules\fdk\node_modules\oauth\lib\oauth2.js:132:9)
    at IncomingMessage.<anonymous> (C:\Users\Ilya\AppData\Roaming\nvm\v10.18.0\node_modules\fdk\node_modules\oauth\lib\oauth2.js:157:7)
    at IncomingMessage.emit (events.js:203:15)
    at endReadableNT (_stream_readable.js:1143:12)
    at process._tickCallback (internal/process/next_tick.js:63:19)
Unfortunately, starting the fdk in the debug mode does not provide any more logs/details of the issue. However, I’ve logged the exact response in the file C:\Users\Ilya\AppData\Roaming\nvm\v10.18.0\node_modules\fdk\node_modules\passport-oauth2\lib\strategy.js on line 358 and it is the following:
{
    error: {
        message: 'Error validating verification code. Please make sure your redirect_uri is identical to the one you used in the OAuth dialog request',
        type: 'OAuthException',
        code: 100,
        error_subcode: 36008,
        fbtrace_id: 'Amd6GY4kmzoEhCIoAZe3aIz'
    }
}
How can I check what redirect_uri is sent in a request to the 3rd-party platform?
As for the OAuth config - it is working fine in the currently available version of the marketplace app. The only differences from the marketplace version in my local tested are the client_id and client_secret due to some 3rd party platform specific security settings, this is why a duplicate “test” version of the app has been created for development purposes in order to work with http://localhost:10001/custom_configs (see the “In development” switch in the top left corner of the screenshot).
I have been using the client_id and client_secret from it for local testing for a couple of years already.
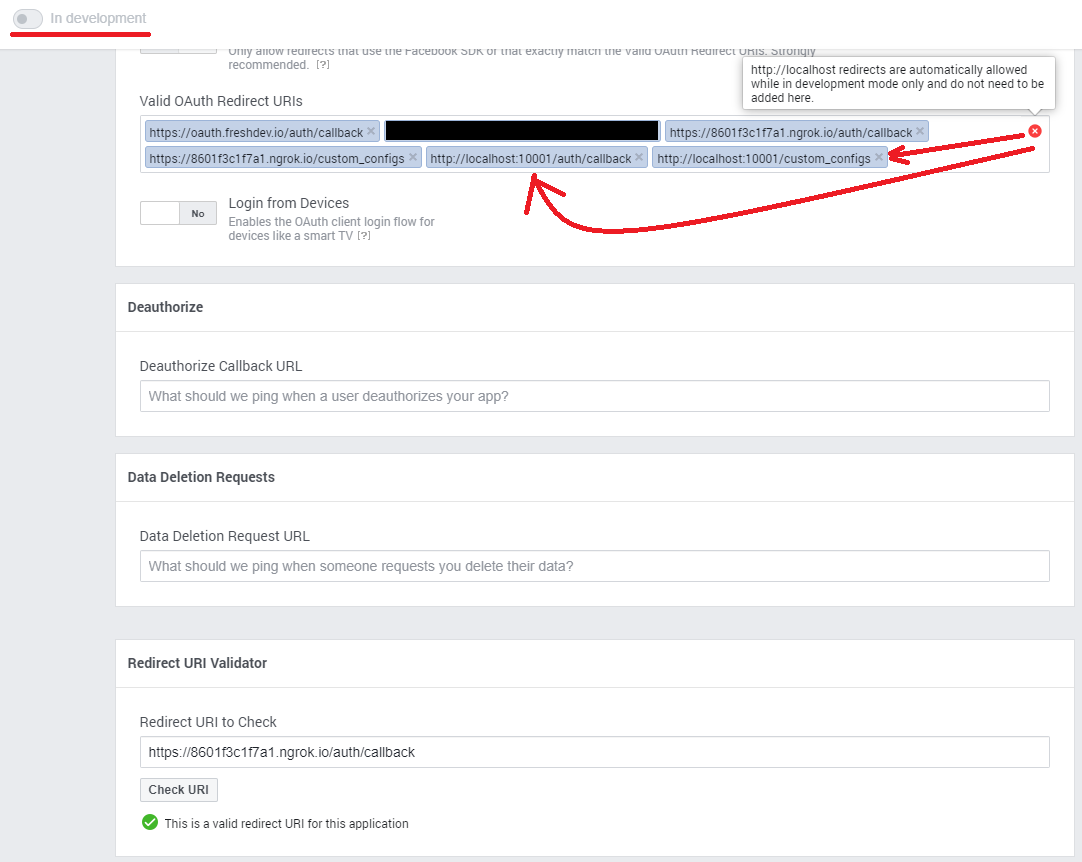
I’ve tried specifying different Redirect URLs, but this didn’t help. I’ve also checked this on a different machine and, unfortunately, the results are the same.
I’ve seen threads with similar issues here (thread #1, thread #2), but my case seems to be a bit different.
Can this be related to the recent platform security updates / OAuth template changes?
Could you please help with this?
 All the screenshots and info you shared so far were helpful to understand what isn’t working.